Project · 2026
Zaleo Auth
One account for every app, without the redirects
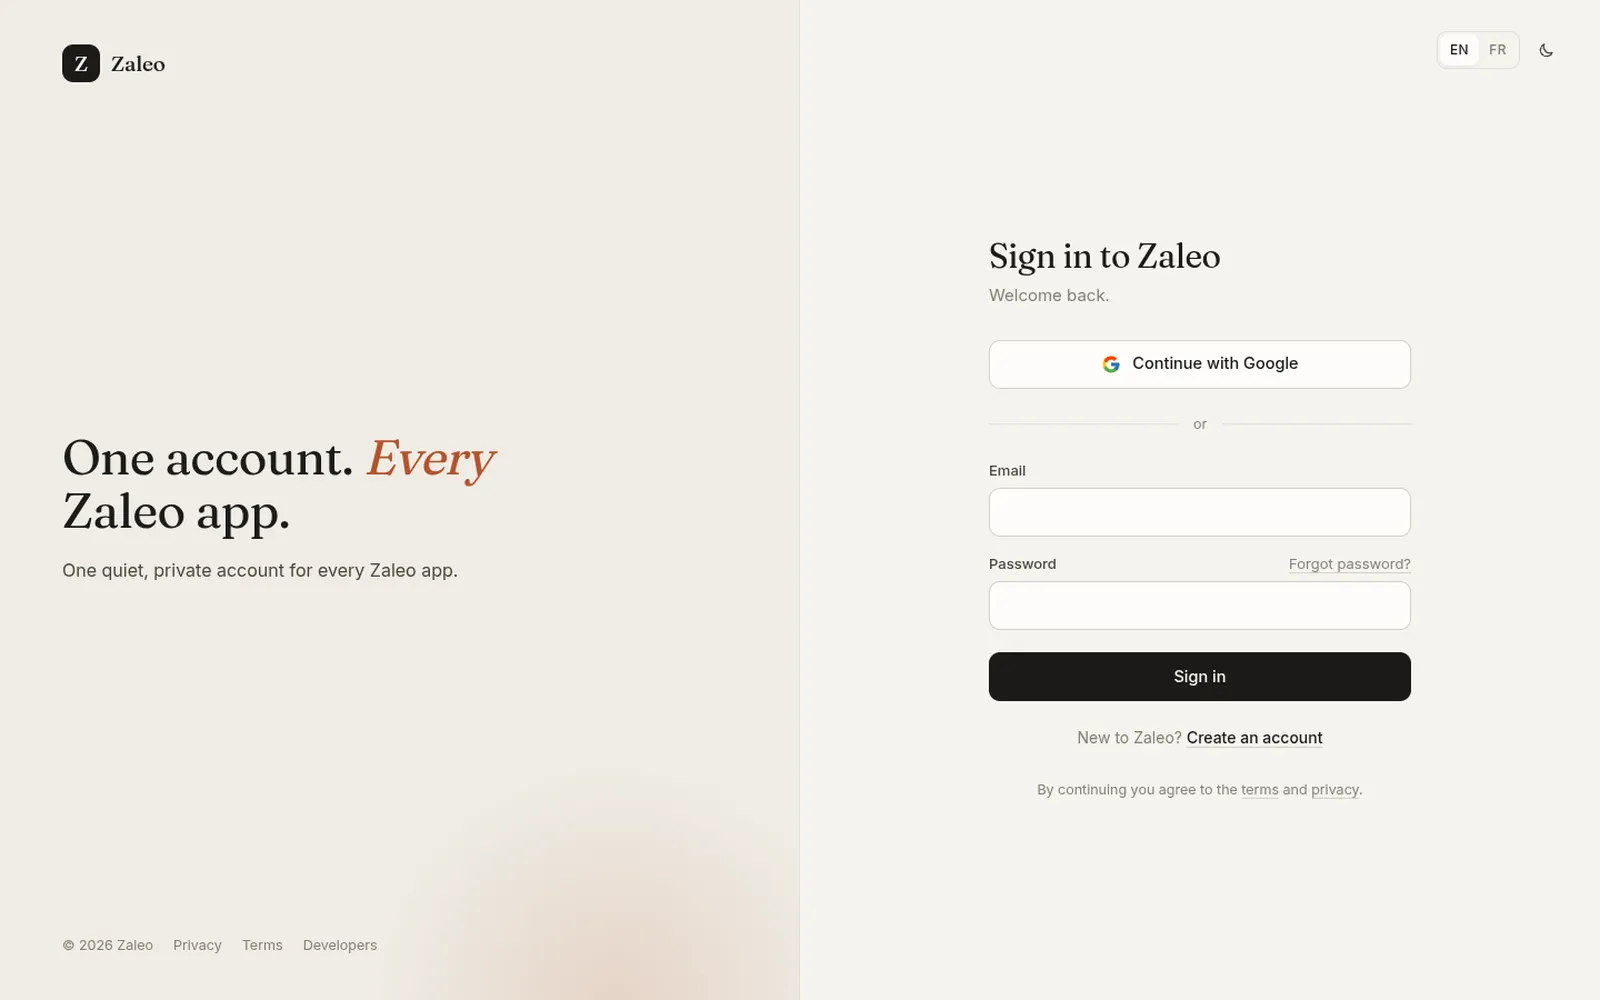
The sign-in behind every Zaleo app, from Kàddu and Suuf to Dawah and Yégle. It is a full OpenID Connect provider, but apps on zaleo.dev never send people away to it: each app shows its own sign-in form in its own design, and the shared session arrives as a short-lived signed token that app servers check offline.
What's interesting about it
- Better Auth on Hono and PostgreSQL: email and password, Google, and verification and reset emails through Resend.
- Embedded mode: one cookie on .zaleo.dev, CORS limited to the registered apps, and a 15-minute RS256 JWT that backends verify against the public JWKS, with no call home per request.
- A small kit (@zaleo/auth) gives each app the forms, the account menu and server helpers, worded in the app's own name.
- Locked down: only the operator registers apps, and every client-management endpoint is disabled.
- Classic OIDC redirects still work for apps outside zaleo.dev.